NEWS
French Supermarket Fridges Spoiled Food After a Forced Defrost
Hackers left French supermarket defrost heaters on all night, and the remote watch sold to save food is the same door CERT-FR now wants shut.

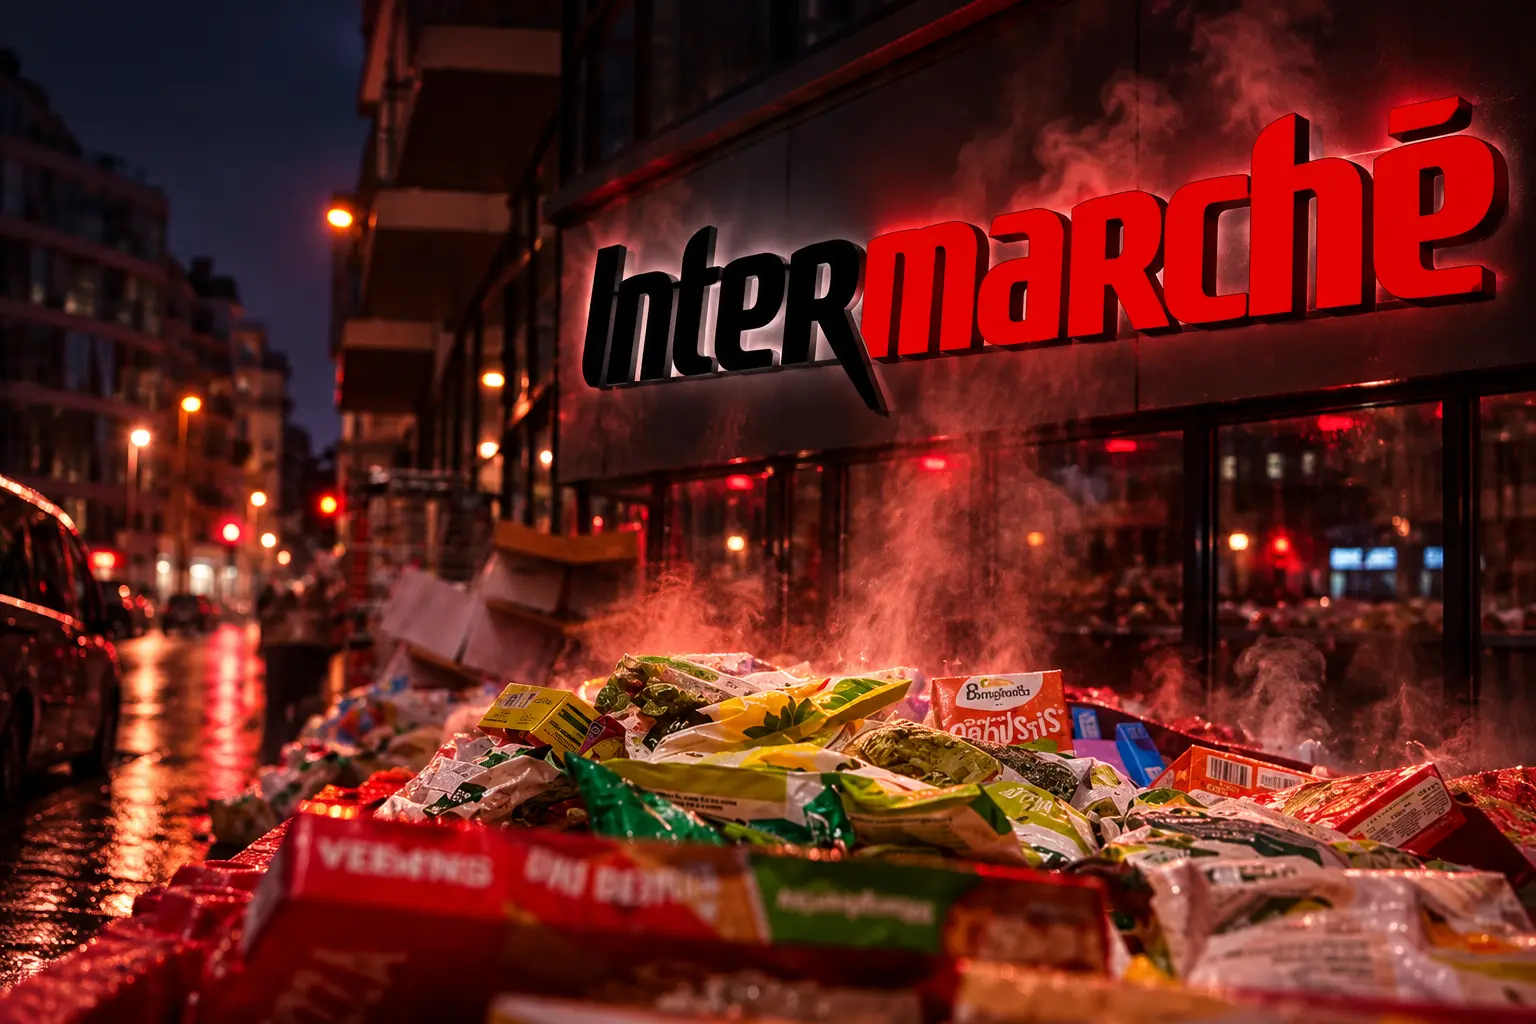
Hackers forced supermarket refrigeration systems across France into an all-night defrost on October 11, sending some cases toward 50°C (122°F) and dumping frozen stock in the street.
France’s computer emergency team later named three controller brands, told shops to take management consoles off the public internet, and warned that attack campaigns were probably still running.
A Defrost Cycle That Never Stopped
The intrusion did not lock tills, steal card data, or flash a ransom note. Attackers reached the boxes that already knew how to melt frost on evaporator coils, then left that cycle on while the stores were closed.
Les Mousquetaires, which owns Intermarché and Netto, said refrigeration units ran at 50°C for six hours. Security researcher Lukasz Olejnik described staff opening freezers in the morning and meeting a wave of hot air, with the target temperature set to 50°C.
The Paris prosecutor’s office said its cybercrime division was working to identify victims and to establish a link between the attack and damage reported as food spoilage and fires. No group has claimed the job, and investigators have said they have not identified the culprits.
Julien Fréret, a supermarket manager in a small town in northern France, said the shop had a total loss of fresh and frozen products. “We never thought we’d see this in our rural setting,” he said, adding, “Don’t bother going to our shop today because we have to put it all in the rubbish.”
What CERT-FR Named on October 13
CERT-FR, the incident team inside France’s National Cybersecurity Agency, published alert CERTFR-2026-ALE-012 on October 12 and revised it the next day. The first version focused on Danfoss AK-SM and AK-SC remote controllers. The October 13 update added Copeland xweb and Dixell xweb units to the same compromise list.
CONTROLLER FAMILIES IN THE FRENCH ALERT
| Product family | When CERT-FR listed it | How it showed up in the incident |
|---|---|---|
| Danfoss AK-SM series | October 12 | Includes older AK-SM800 managers and current AK-SM 800A units on old firmware |
| Danfoss AK-SC series | October 12 | Includes the AK-SC355, named by Danfoss among legacy hit units |
| Copeland xweb | October 13 | Added after the first night, as a separate remote controller family |
| Dixell xweb | October 13 | Added the same day; Coopérative U later said its shops are not Danfoss clients |
The bulletin’s plainest line is the one the industry already knew and had not closed. Exposing a management interface on the internet, CERT-FR wrote, runs against good practice. It also told operators to inspect configuration in full, including defrost ranges, which is the function the attackers left running.
WHAT CERT-FR TOLD OPERATORS TO DO
- Internet exposure: Pull those consoles off the public internet, including every unit on a public IP address.
- Insurance check: Read the contract before cutting the internet data feed back to the refrigeration contractor.
- Defrost settings: Verify the whole configuration, especially defrost time bands.
- Remote access: Bring the console back only through a secure VPN or a protected network; a quick firewall allow-list for the contractor is an emergency step, not a lasting one.
- Compromised boxes: Factory-reset, then rebuild the setup; on end-of-life gear with no patch, a reset alone is not enough because the unit can be taken again.
A person close to Prime Minister Sébastien Lecornu said ANSSI had identified a flaw in software from the Danish vendor, contacted that vendor, and alerted European counterparts because other countries may use the same kit.
Danfoss Says Most Hit Units Were Off Support
Danfoss, the Danish maker of supermarket refrigeration controls, said it was aware of incidents in France affecting a limited number of refrigeration management systems. Most of the affected equipment, the company said, was legacy product that no longer receives software or security updates, or current product running outdated firmware.
It named the AK-SM800 and AK-SC355 system managers, and said an affected version of the AK-SM800 was on old firmware. Kirsten Tate, a Danfoss spokeswoman, said the company has long advised customers to keep supported systems updated with the latest firmware, and that it was in close contact with affected customers.
That answer puts the first bill on the shop that kept an unsupported box on a live line. It does not settle how the attackers got in. Authorities have not confirmed that bugs patched in 2025 were the path used in October, and CERT-FR’s second-day list already reached beyond Danfoss.
The 2025 Paper That Used the Word Defrost
Tomer Goldschmidt of Claroty’s Team82 spent last year on the Danfoss AK-SM 800A, the current system manager that sits above a store’s cold cases and talks to them through an embedded web console called StoreView. The paper the team published after Danfoss shipped a fix is titled “Freeze the Controller, Defrost the Food.”
Team82 did not need a stolen badge to start. Searching Shodan and Censys for the StoreView signature, the researchers found thousands of publicly reachable StoreView consoles. A Censys scan in that research showed 2,765 exposed AK-SM 800A devices.
From there they rebuilt a hidden “code of the day” login that built a password from the device’s date and time, a command-injection bug in the alarm-to-mail settings, and a way to push new Nginx headers that could knock the web service over. Danfoss credited Goldschmidt on advisory DSA-2025-08-01, published August 1, 2025, and told customers to install the 4.3.1 firmware patch on AK-SM 8xxA units.
BUGS PATCHED ON THE CURRENT AK-SM 8XXA LINE
- CVE-2025-41450: A datetime-based password that bypassed login on versions before R4.2, scored 8.2 under CVSS v3.1.
- CVE-2025-41451: Command injection in alarm-to-mail fields on versions before 4.3.1, scored 8.7 under CVSS v4, with a path to code execution after login.
- CVE-2025-41452: Authenticated Nginx configuration injection on versions before 4.3.1, scored 6.8 under CVSS v4, with a denial-of-service path.
CISA logged those flaws against commercial facilities, said the equipment is deployed worldwide, and repeated the same network rule CERT-FR would later put in an emergency alert: do not leave control-system devices reachable from the internet. Paris firm Synacktiv said on October 13 that its researchers had already flagged an authentication bypass on Danfoss SM800 and SC355 controllers in 2023.
THE YEAR THE COLD CASES WERE ALREADY IN THE ADVISORIES
- May 20, 2025: CISA publishes the first AK-SM 8xxA advisory, covering the login bypass later tagged CVE-2025-41450.
- August 1, 2025: Danfoss publishes DSA-2025-08-01 and points supported customers at firmware 4.3.1.
- August 26, 2025: CISA Update A adds CVE-2025-41451 and CVE-2025-41452 and still records no known public exploitation of those bugs.
- October 11, 2026: Attackers force defrost cycles on supermarket controllers overnight into October 12.
- October 12, 2026: CERT-FR confirms numerous compromises of Danfoss AK-SM and AK-SC remote controllers.
- October 13, 2026: CERT-FR adds Copeland xweb and Dixell xweb and says campaigns are probably still under way.
More than a year sat between the 4.3.1 patch and the Sunday night heat. That gap does not prove which bug, if any, was used. It does show how long a store could keep a known-weak console on a public address after the fix existed for the current line, and how little help a patch is to the older AK-SM800 and AK-SC355 boxes Danfoss no longer updates.
Independent Owners Took the First Losses
The chains did not publish one national total, and adding their figures would mix counts taken on different days. Each group’s own tally is the clean record of who got hit.
WHAT EACH GROUP HAS CONFIRMED
| Group | Stores hit | What the group said about the damage |
|---|---|---|
| Les Mousquetaires (Intermarché, Netto) | About 300 | Units ran at 50°C for six hours; fresh and frozen stock had to be thrown out |
| Coopérative U | 80 of nearly 2,000 | Most sites stopped a cold-chain break; where they could not, the food was pulled and destroyed |
| Carrefour | 80 of about 6,000 | Confirmed a hit on a small slice of the network |
| Monoprix | About 5 percent of roughly 490 French stores | Groupe Casino said no other Casino banners were affected |
Dominique Schelcher, chief executive of Coopérative U, declined to put a group-wide price on the night. He said a failing refrigeration system could cost a small supermarket tens of thousands of euros, and a hypermarket as much as €200,000 (about $220,000). Two shops in Haguenau, in Alsace, recorded combined losses of €270,000.
Outside an Intermarché in Paris on Tuesday, a worker filled boxes with food that had passed its safe life. That pile is the bill the software vendor does not carry. Independent owners hold the inventory. Growers who sent the week’s crop into those cases are the next silent party, watching product they already harvested go into the rubbish for a fault in a controller they never bought.
CERT-FR’s insurance line is the tell that the money fight started before the freezers were even back on. Operators were told to check policy terms before they cut the contractor’s remote feed, because the same link that let a technician watch temperatures at 3 a.m. is the link an insurer may treat as a condition of cover.
Why the Fridges Stayed on the Public Internet
Schelcher spent Tuesday defending the architecture that had just failed him. U’s refrigeration plant, he said, is connected to the internet so staff can watch temperatures day and night and move fast when a case drifts. He called that link essential to keeping food sound.
They’re attacking the French people’s food supply. In my entire professional career, I’ve never seen anything like this.
Dominique Schelcher, chief executive of Coopérative U, on RTL
On RTL he also said U shops are not Danfoss customers, which fits CERT-FR’s second-day turn toward Copeland and Dixell. His J+1 note on X put the U count at 80 of nearly 2,000 points of sale and said most teams had blocked a break in the cold chain.
Cyberattaque J+1
Au lendemain de la cyberattaque qui a touché les installations frigorifiques de plusieurs enseignes de la grande distribution, je souhaite revenir sur les faits et faire un premier point de situation concernant nos magasins @cooperativeu.
80 magasins de notre… pic.twitter.com/GijWQZF1lC
— Dominique Schelcher (@schelcher) October 13, 2026
Connecting a case for a night watch is a food-safety argument. Leaving the management console on a public address is a different choice. Replies under Schelcher’s post split those two ideas in one beat: the socket can exist, and it still has to sit behind a firewall. One farmer wrote that it was crushing to see the fruit of that work thrown away. The first physical loss in this attack is wet cardboard, not a leaked database.
Open Consoles and a Campaign Still Under Way
CERT-FR’s October 13 warning was written in the present tense. Attack campaigns against these controllers were probably still running. An unsupported unit left on the internet, the alert said, faces a high chance of compromise; a factory reset wipes a live infection and leaves the same hole open for the next pass.
CISA had already filed the AK-SM 8xxA family under commercial facilities and noted that the gear is in use worldwide, with the vendor based in Denmark. ANSSI’s outreach to European partners is the official admission that a French Sunday night is not a closed geography problem.
The prosecutors still have to name a culprit and prove the path from a remote setting change to spoiled food and to the fires shops reported. Until that file closes, the working record is simpler. A defrost function built to protect food ran until the food was ruined, on consoles that vendors, researchers, and now CERT-FR had already said should not be sitting on the public internet.

Ohtani Game 4 Logoman Card Sells for $3.24 Million

Cole Kmet’s Season Ends, and Chicago’s Tight End Plan Starts

NBA Seeks Soccer Money After EuroLeague Clubs Refused

Amazon’s First Bond Tests Leave the Broccoli Chair Empty

Tyrese Maxey Owns the Night Built for LeBron James

Warsh Rejects Rate Guidance and Still Moves Markets

Dana-Farber Exits an MGB Medicare Advantage Network Early

NASA Launches the Roman Space Telescope’s Cosmic Bet

OpenAI’s Cyber Letter Puts the Defense Bill on Governments

Russia Recycles Its Old Warning Over Storm Shadow Plants
-
 BUSINESS2 months ago
Warsh Rejects Rate Guidance and Still Moves Markets
-
 BUSINESS1 month ago
Dana-Farber Exits an MGB Medicare Advantage Network Early
-
 NEWS2 months ago
NASA Launches the Roman Space Telescope’s Cosmic Bet
-
 NEWS2 months ago
OpenAI’s Cyber Letter Puts the Defense Bill on Governments
-
 NEWS2 months ago
Russia Recycles Its Old Warning Over Storm Shadow Plants
-
 ENTERTAINMENT4 weeks ago
Primetime’s $2.7 Million Preview Tops Pitt’s Costlier Film
-
 BUSINESS2 months ago
Jet Drones Lock Down Kyiv and Strip Kherson of Heat
-
 ENTERTAINMENT2 months ago
Midnight Spider-Man Turns Peter Parker Into Oscorp’s Hybrid