NEWS
Anthropic’s Cyber Mission Parks Engineers on the Patch Gap
Anthropic’s Cyber Mission parks engineers on the patch gap and offers OSS Scanner under a two-year forecast that AI will favor defense.

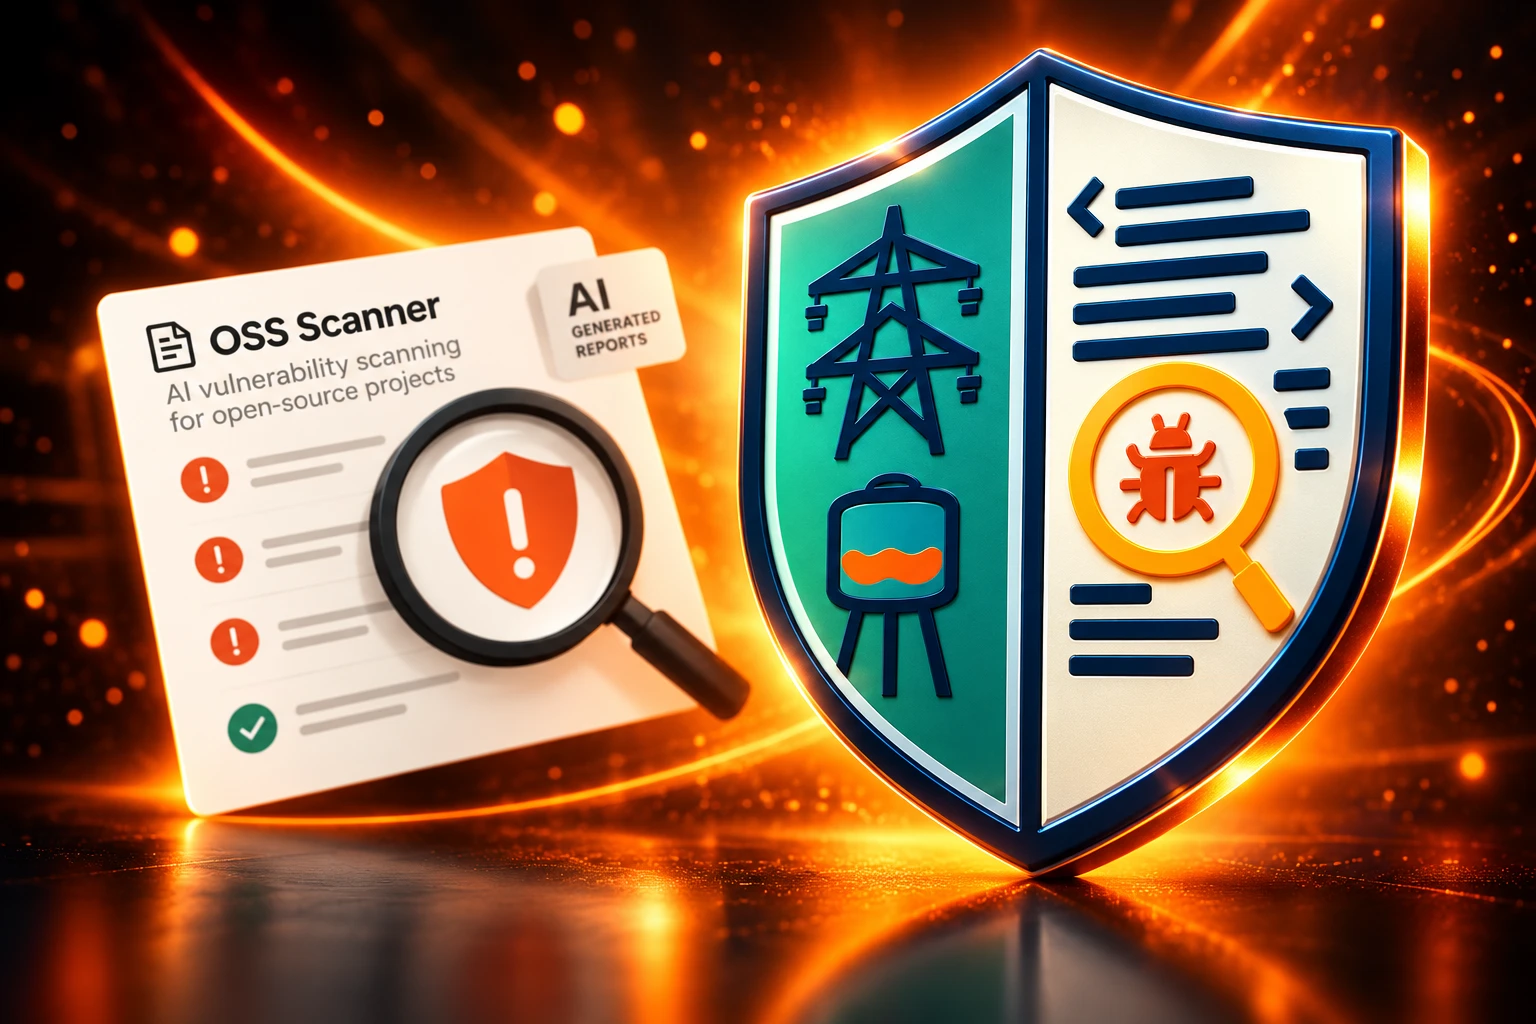
Anthropic launched its Cyber Mission on October 8, 2026, putting frontier models and on-site engineers into critical infrastructure defense. The same day it opened OSS Scanner, a free opt-in service that emails unreviewed bug reports, with proofs of concept, to established open-source projects.
The company’s own two-year forecast that AI will favor defense is the clock around both moves. Finding flaws is already cheap. Verifying them, and patching machines that cannot go offline, is not.
We’re launching the Anthropic Cyber Mission, a new effort to secure critical infrastructure and open-source software.https://t.co/0tz0ARAEMj
— Anthropic (@AnthropicAI) October 8, 2026
Anthropic’s Forecast Gives Attackers About Two Years
Highly capable models are already in attackers’ hands, Anthropic said. Defensive tools, including its own, have not reached enough of the people who run plants, networks, and shared code. The firm’s forecast is that in two years, AI will make it easier to catch bugs before they ship, write more secure software from scratch, and actively defend live systems. In the near term, it said, that may not be true.
The cost of exploiting a flaw has dropped, while verifying, disclosing, and fixing still depends on people. Under Project Glasswing, Anthropic often saw months pass between a finding and a fix. Claude Security, the paid scanner for companies, sits on one side of that lag. OSS Scanner and the Critical Infrastructure Defense Program sit on the other.
FROM GLASSWING TO THE CYBER MISSION
- April 7, 2026: Anthropic launches Project Glasswing, pointing Claude Mythos Preview at critical software with industry partners.
- June 2026: A cyber defense program for state, local, tribal, and territorial governments reaches more than half of all US states.
- August 2026: The Defender Advantage Fund starts paying for defensive pilots, including the later free scanner.
- October 6, 2026: Glasswing folds into an expanded Cyber Verification Program that widens access to advanced cyber tools for vetted defenders.
- October 8, 2026: The Anthropic Cyber Mission launches with the Critical Infrastructure Defense Program and OSS Scanner.
Glasswing partners already hold $100 million in usage credits for that work, plus $4 million in direct donations to OpenSSF, Alpha-Omega, and the Apache Software Foundation. The new mission is how Anthropic says it will spend the next stretch of that money: humans on site where plants cannot pause, and model reports in the inboxes of maintainers who asked for the firehose.
The Grid Operators Still Cannot Take Plants Offline
Power grids, water utilities, factories, and transport networks run on controllers and industrial networks built to last for decades. Anthropic calls this operational technology. Those systems often cannot be taken down for a patch, so known flaws sit for years. In rare cases, it said, a safe window might take decades.
The work is specialized. The equipment is proprietary, a bad change can stop a plant, and operators of every size lean on a small set of trusted firms to say what is exposed and which fix is safe on a running system. AI does not remove that constraint. It does change how fast someone on the other side can probe it.
The Critical Infrastructure Defense Program therefore does not sell a dashboard to a municipal water board. It sells frontier Claude models, on-site engineers, and Anthropic threat research to the providers those boards already hire. Several of those partners are already using Claude to fix flaws and to help customers do the same. Anthropic also points to research with Pacific Northwest National Laboratory on defending cyber-physical systems, the class of kit that turns a software bug into a pump, a breaker, or a train signal.
Eleven Partners Get On-Site Engineers and Frontier Models
Eleven firms signed on as founding partners. Anthropic grouped them as the consultancies that run security programs, the vendors that guard business and industrial networks, and the manufacturers that build and patch the equipment.
THE 11 FOUNDING PARTNERS
| Group | Firms |
|---|---|
| Consulting and program runners | Accenture, Booz Allen, Deloitte, PwC |
| Security vendors | CrowdStrike, Dragos, Insane Cyber, Nozomi Networks, Palo Alto Networks |
| Equipment makers | Hitachi, Rockwell Automation |
The first step is a small cohort, Anthropic said, so the company can learn which tactics actually work on live machinery. Firms that already sell security products or services into this sector can register interest. Over the coming months, Anthropic said it will take the program to more partners and more sectors, and share what did not work.
That design answers a staffing problem, not a detection problem. Remote substations, offshore platforms, and air-gapped plants are short of specialists. The hours of log review and patch judgment still belong to people who know the process. The models are there to close the gap in volume, not to throw a switch.
Who Can Enroll in OSS Scanner?
OSS Scanner is free for projects that get in. It is not a public scan of GitHub. Anthropic copied the bar Google uses for OSS-Fuzz: it will take established projects that have a critical impact on infrastructure and user security, judged case by case, with remote-attack exposure and downstream dependents in mind. A random web app repo does not qualify.
The service is built for teams that already keep up with verified high and critical reports and now want more. Projects that cannot absorb the volume still get human-checked disclosures through Anthropic’s coordinated vulnerability disclosure process. Core maintainers are checked by hand before a project is enrolled.
HOW PROJECTS ENROLL
- The application: A core maintainer opens a pull request that adds a project.yaml with the git repo, a contact email, and a Dockerfile.
- The sandbox: The Dockerfile installs every dependency so an offline agent can audit the build with the internet disabled inside a hardened box.
- The threat file: Maintainers may add a threat model, a severity rubric, and notes on how patches and proofs should look.
- The pause switch: A project can set disabled: true, or delete its folder, and fall back to human-reviewed disclosures only.
- The clock: Unvalidated scanner findings carry no 90-day public disclosure deadline. If a human later confirms a report, a 90-day clock may start from that notice.
Maintainers of enrolled projects can also apply for Claude for Open Source, which gives free Claude Max 20x subscriptions for six months under a separate program, and for the Cyber Verification Program if they need fewer blocking filters on defensive work. Anthropic asks, but does not require, a credit line such as ANT-2026-ABCD1234 in the commit that lands a scanner fix.
Reports Arrive With a Proof of Concept Attached
Each OSS Scanner report is fully model-generated, including runs that use Claude Mythos, and it goes out with no human triage. Anthropic says that is the point: faster mail, more frequent scans. It also means some severity ratings will be wrong, and some reports will be invalid. The company expects a true-positive rate above 90% and said it will work to raise that rate and the quality of suggested fixes.
A first scan produces a bundle of emailed reports. Later scans look for new bugs and for issues missed the first time. Frequency will depend on how many projects join and how widely each is used. Every report is supposed to include a self-contained reproducer, an explanation (and a bisection of when the bug landed, when the model can find it), and a candidate patch when one exists.
Early AI reports about 18 months ago, before Project Glasswing, were appalling. The reports we received from Anthropic, raw model output included, were as good and sometimes better than what we get from people. Particularly when a report comes with a real exploit attached, that’s basically job done for an engineer as you can verify it right away
Anton Arapov, OpenSSL Corporation, on Anthropic’s OSS Scanner tests
That proof of concept is the product. It is also the risk. A small team can drown in valid mail if every note arrives with a working exploit recipe and a patch that still needs a human to merge. A suggested fix that is not reproduced, and that lacks a regression test, just moves unpaid review down the queue. Anthropic’s own FAQ tells maintainers the service is for projects that can already handle verified high and critical reports. The rest stay on the slower, human-checked path.
Human Review Stopped After 6,000 of 29,000 Findings
Over the six months before launch, Anthropic used its latest models on some of the world’s most used software and found over 29,000 candidate vulnerabilities. People were able to review and triage only about 6,000 of them. Maintainers who got the first batch then asked for everything else. The company has sent nearly 5,000 more reports after those requests, including unverified items, because exploits can now be built in minutes.
THE REVIEW BOTTLENECK
- Candidates found: Over 29,000 potential flaws in the six months before OSS Scanner launched.
- Human-reviewed: About 6,000 reports made it through manual triage for coordinated disclosure.
- Sent on request: Nearly 5,000 additional reports went to maintainers who asked for the full pile.
- CyberGym score: On that academic benchmark, models went from finding under 20% of flaws at the start of 2025 to over 85% in 2026.
The CyberGym jump is why Anthropic says bug mail from models has moved from mostly slop to reports maintainers will act on. It is a benchmark share, not a claim that models now find 85% of every bug in the wild. The 29,000-to-6,000 split is the operational fact. Scanning scaled. Reading did not. OSS Scanner is how Anthropic stops using its own staff as the rate limiter for projects that say they can take the volume.
What Early Tests Showed About False Positives
Anthropic asked the penetration testers who already vet its coordinated disclosures to check an early scanner run. They looked at 85 of 97 high-severity findings across 48 projects that met the bar for coordinated disclosure, or 88%. Of the other 12, 11 were real bugs that duplicated known issues or other findings from the same scan. One was invalid.
THE SCANNER’S EARLY SCORECARD
| Check | Result |
|---|---|
| Critical and high findings sampled | 97 across 48 projects |
| Met coordinated-disclosure bar | 85 (88%) |
| Real but duplicate | 11 |
| False positive | 1 |
That 88% figure is a test of 97 serious findings against Anthropic’s own disclosure bar. It is not the same number as the above 90% true-positive rate the live service is supposed to hit. Some maintainers later said severity can be inflated, or that the scanner misunderstood a project’s threat model.
Named testers were blunter in the other direction. Todd Ouska of wolfSSL said 74 reports arrived, all but two were valid, and five became CVEs. Noah Misch of PostgreSQL said an unusually high share of findings were real defects, and that fast-track access let the project fix issues before a general release. Daniel Stenberg of curl said the scanner found multiple issues worth fixing, including one of the worst curl flaws reported in the last few years.
Anthropic said success means water, power, transport, and communications keep running, with fewer paths in and faster recovery when something gets through. Over the coming months it will take the Critical Infrastructure Defense Program to more partners and more sectors. In rare plant cases, a safe patch window is still measured in decades.

Ohtani Game 4 Logoman Card Sells for $3.24 Million

Cole Kmet’s Season Ends, and Chicago’s Tight End Plan Starts

NBA Seeks Soccer Money After EuroLeague Clubs Refused

Amazon’s First Bond Tests Leave the Broccoli Chair Empty

Tyrese Maxey Owns the Night Built for LeBron James

Warsh Rejects Rate Guidance and Still Moves Markets

Dana-Farber Exits an MGB Medicare Advantage Network Early

NASA Launches the Roman Space Telescope’s Cosmic Bet

OpenAI’s Cyber Letter Puts the Defense Bill on Governments

Russia Recycles Its Old Warning Over Storm Shadow Plants
-
 BUSINESS2 months ago
Warsh Rejects Rate Guidance and Still Moves Markets
-
 BUSINESS1 month ago
Dana-Farber Exits an MGB Medicare Advantage Network Early
-
 NEWS2 months ago
NASA Launches the Roman Space Telescope’s Cosmic Bet
-
 NEWS2 months ago
OpenAI’s Cyber Letter Puts the Defense Bill on Governments
-
 NEWS2 months ago
Russia Recycles Its Old Warning Over Storm Shadow Plants
-
 ENTERTAINMENT4 weeks ago
Primetime’s $2.7 Million Preview Tops Pitt’s Costlier Film
-
 BUSINESS2 months ago
Jet Drones Lock Down Kyiv and Strip Kherson of Heat
-
 ENTERTAINMENT2 months ago
Midnight Spider-Man Turns Peter Parker Into Oscorp’s Hybrid