NEWS
Europe’s Freezer Hacks Hit the Shops That Stayed Online
Supermarket freezer cyber-attacks hit 10 countries on November 2 because remote Danfoss and Copeland panels were still on the public internet after France.

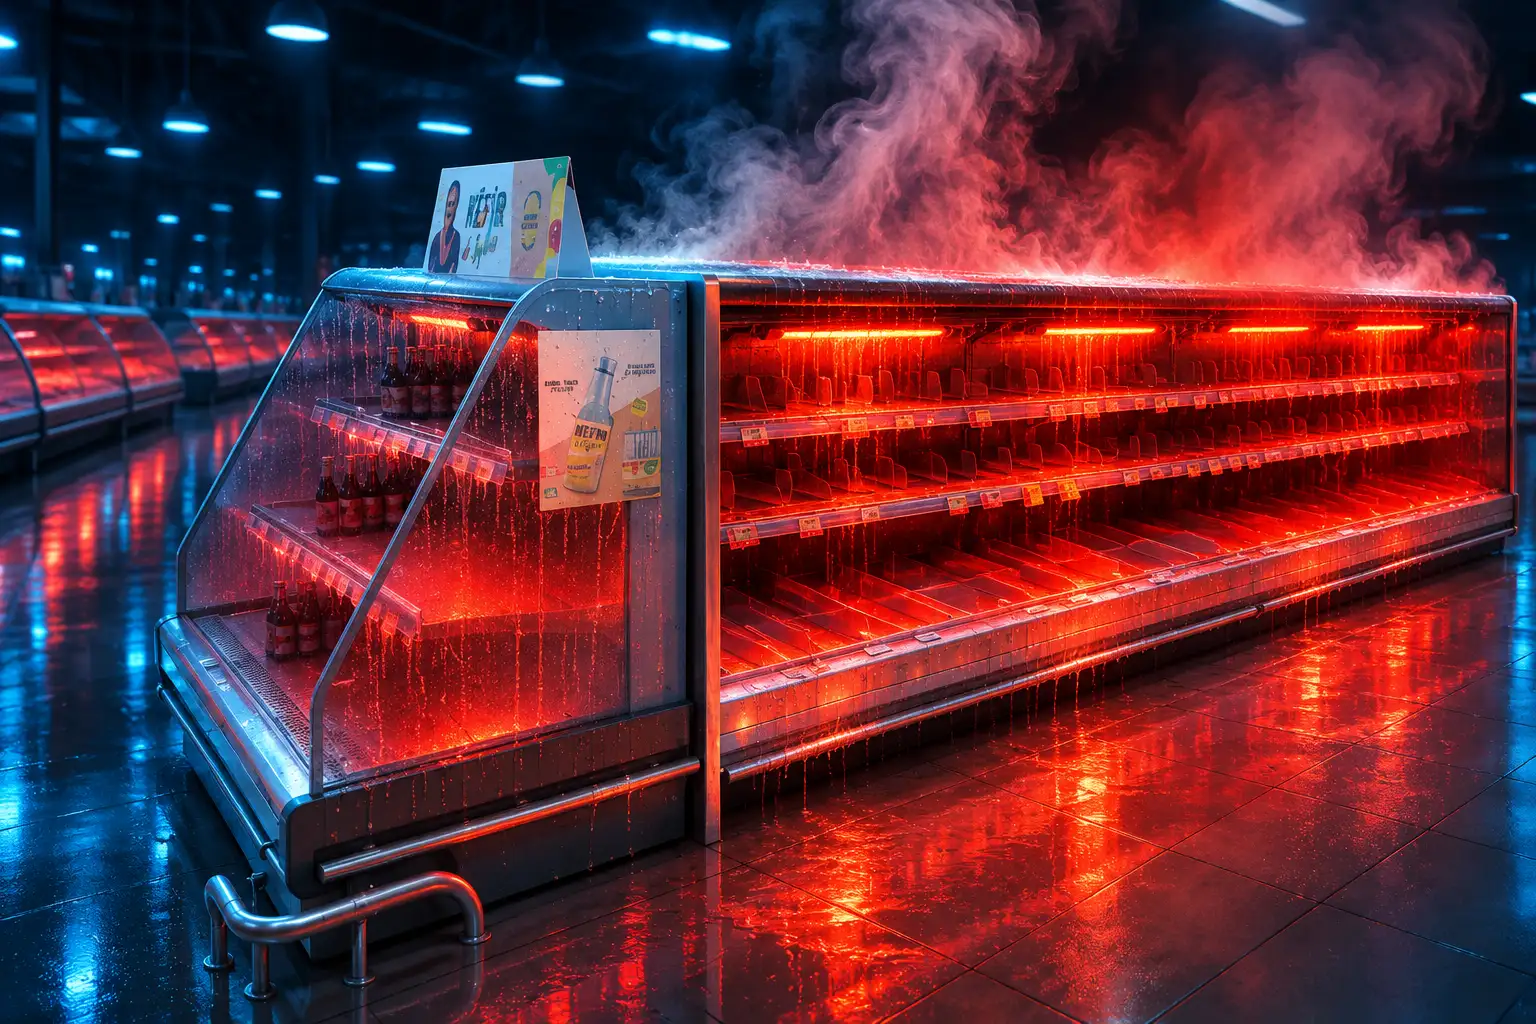
Hackers pushed supermarket freezers to 50C (122F) in at least 10 European countries on November 2, three weeks after France had the same attack. Staff opened chilled aisles to thawed meat, wet cardboard and alarms that had been delayed by forced defrost cycles. No group has claimed the work.
The shops that still left remote fridge panels on the public internet paid a bill France had already posted. Danish maker Danfoss had told customers on October 13 to cut those boxes off the open net. Most stores did. A small number did not.
Overnight Defrosts Hit Stores in 10 Countries
Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal, Germany and Sweden all reported cooling failures overnight into November 2. Industry tallies put the new wave at more than 100 stores. Temperatures in some cabinets were driven as high as 50C, the same mark used in France.
THE NOVEMBER 2 WAVE
- The heat: Attackers forced evaporators into defrost and raised set points until chilled and frozen stock had to be thrown out.
- The countries: Failures were logged in 10 states, with extra UK cases flagged separately by the National Cyber Security Centre.
- The stores: More than 100 shops were hit, with Belgium the hardest and small butchers in the Netherlands among the named victims.
- The claim of credit: None. Belgian federal prosecutors have opened a case and national cyber teams are still mapping the path in.
About 40 Delhaize shops in Belgium and Luxembourg lost cooling, and 15 of Carrefour’s 700 Belgian stores were hit, along with Spar outlets and an Ikea in Mons. Ireland’s Musgrave Group pulled chilled and frozen lines from 13 SuperValu stores out of 223, then said the incident was fully resolved by the next afternoon. Danfoss told Dutch media that at least 17 businesses there were attacked, mainly butcher shops and small grocers rather than the big chains.
Portugal’s Mosqueteiros group linked seven Intermarché stores to an outside firm that managed their cooling. Italy’s cyber agency counted at least four Coop shops in Sicily and one business in Tuscany. Giorgia Meloni’s office said the impact was currently very limited and that the hit sites were mostly still on obsolete security, with interfaces directly exposed to the internet and weak logins. Germany logged three shops, including a Rewe in Raesfeld that named a cyber-attack on system provider Danfoss and was running again by Monday afternoon, plus an Edeka in Reisbach and a CAP store in North Rhine-Westphalia.
Sweden’s ICA said a limited number of stores outside its central network had trouble, and Coop reported units tied to a 4G mobile link that made them easier to reach. Finland’s Kesko said a few smaller shops saw irregular temperatures. Estonia’s Kitman Coldtech said attackers reached a computer that controlled a client’s older Danfoss kit and raised it to 50C, and that the change was caught within minutes.
France Already Paid This Bill in October
The method was not new. Overnight from October 11 into October 12, attackers seized remote fridge controllers in France, stretched defrost cycles, and cooked stock. The Paris prosecutor’s office said the attack caused food losses and fires. Intermarché chief Thierry Cotillard put nationwide losses in the tens of millions of euros in a single day.
Carrefour said 80 of its French stores were hit. Les Mousquetaires said around 150 Intermarché stores were heated to 50C for six hours. Cooperative U chief Dominique Schelcher said 80 of about 2,000 shops in his network were targeted and called the attack, in his words, of utmost gravity. As many as 700 French grocery stores were affected in all.
THE THREE-WEEK CLOCK
- October 12, 2026: France’s CERT-FR publishes alert CERTFR-2026-ALE-012 on numerous compromises of Danfoss AK-SM and AK-SC remote fridge controllers.
- October 13, 2026: CERT-FR adds Copeland xweb and Dixell xweb. Danfoss tells customers to drop public internet links and come back only through a secure network.
- October 14, 2026: Internet scans show French StoreView panels falling from 1,825 on October 11 to 537, a 71% drop, as operators yank interfaces offline rather than only patch them.
- October 16, 2026: CERT-FR updates its advice and warns that attack campaigns are probably still under way, and that an end-of-life box left on the internet is very likely to be taken again.
- November 2, 2026: The same overnight defrost pattern hits stores in 10 countries. Danfoss says most shops acted in October, but a small number did not.
Stephan Moelans, chief of Belgian refrigeration firm Sabcobel, which runs Delhaize’s systems, said the November blow could have been far worse if his side had not started patching after the French attack. Sabcobel said the attackers got into individual shops rather than the contractor’s own core. That split, shop by shop, is why a national chain can look fine while a franchise freezer in the same banner cooks overnight.
The Login Code Was the Date
The boxes that run a supermarket cold aisle are not simple thermostats. Danfoss AK-SM 800A units sit as the shop-floor control centre: they watch circuits, set temperature limits, fire alarms, and let a contractor change schedules from a browser. Claroty’s Team82 lab spent 2025 and 2026 on that web interface and found a hidden code-of-the-day login that skipped the real password, plus a command-injection bug that led to remote code execution after a session was open.
The daily code was built from the device’s date. Anyone who rebuilt the algorithm could mint a valid admin login for that day without knowing the store password. Team82 also found an authenticated path to inject Nginx rules and knock the web service over. Danfoss shipped firmware R4.3.1 that closed the flaws, after an earlier R4.2 build addressed the date-based login. Cryptographer Mathias Hall-Andersen put the practical version in one line: “The password was Hash(CurrentDate).”
U.S. agency CISA listed the same bugs in ICS advisory ICSA-25-140-03, last revised August 26, 2025, and scored the command-injection issue with a CVSS v4 score of 8.7. CISA already told operators to keep control devices off the internet and to use a VPN if remote access is required. CERT-FR later said it had not named a specific bug as the way into the French shops, and neither Danfoss nor French authorities have tied the grocery attacks to those CVEs. What both waves share is simpler: management pages that answered on a public address, often on old firmware, sometimes still on factory passwords.
Danfoss said most French victims were older AK-SM 800 controllers that reached end of life in May 2021, or AK-SC 355 units discontinued in 2016, with some current AK-SM 800A boxes on outdated firmware. End-of-life hardware does not get a new build. A shop that kept those panels on a public IP had no patch path left.
More Than 1,000 Panels Still Face the Open Internet
Internet intelligence firm Censys counted 2,991 StoreView control panels reachable worldwide on October 11, 1,825 of them in France. Three days later the French figure was 537. By Censys’s November analysis France was down to 220, and the firm still found just over 1,000 StoreView panels still online globally, with France first, then Belgium and the United States.
A new wave of cyberattacks on supermarket refrigeration systems has hit more European countries.
Censys ARC currently observes just over 1,000 Internet-exposed Danfoss StoreView instances globally. https://t.co/YlOcKZsCFK #CensysARC
— Censys (@censysio) November 2, 2026
A patch on a box that is still published to the world is not the same as taking the box off the net. Censys found 68% of the StoreView instances still visible in Belgium were on 4.3.1 or later, and 58% in Sweden, yet both countries still had shops cooked on November 2. The scan is not a victim list. It is a map of who left a management page where a stranger could knock.
STOREVIEW PANELS STILL ON THE PUBLIC INTERNET
| Country | Exposed StoreView hosts | Share on patched 4.3.1 or later |
|---|---|---|
| France | 220 | 41% |
| Belgium | 138 | 68% |
| Netherlands | 51 | 37% |
| Sweden | 50 | 58% |
France’s leftover 220 is an 87.9% fall from 1,825, and 45% of those remaining French hosts still looked pre-4.2, the class with the date-based login. The Netherlands, where Danfoss said hit systems were not on a secure network and still used default passwords, had only 37% of visible StoreView hosts on 4.3.1 or later. Censys also saw six hosts in Luxembourg, three in Ireland and two in Estonia, most of them on patched builds, and still on public addresses. Team82, during its earlier research, had already counted thousands of AK-SM 800A management interfaces on open scans, including 2,765 in one Censys pass of that model line.
Small Shops Took the Hit the Chains Avoided
Large banners with central networks came through cleaner than independents. ICA said the Swedish stores that failed sat outside its central link. Dutch chains reported no impact while at least 17 smaller businesses did. SuperValu’s problem was limited to a specific refrigeration model. That pattern matches a contractor model in which each shop’s controller, not the retailer’s head office, is the door.
I don’t even understand how anyone could do this… How can we end up throwing away so much food? I find it truly distressing. In moments like these, you just feel like quitting your job.
Mathieu Tilman, manager, Delhaize supermarket, Belgium
EU food and agriculture commissioner Christophe Hansen said the bloc was taking the incidents very seriously and warned of further disruption. Commission spokesman Thomas Regnier would not pin blame, and said the events show how cyber-attacks can disrupt essential services and affect daily life, and that these are not isolated cases. The political line is food-supply fear. The practical line is a contractor’s browser page that still had a public IP after a continent-wide fire drill.
Why Did the Freezers Answer the Internet?
Remote access exists so a refrigeration firm can watch temperatures, change defrost windows, and skip a van visit. CERT-FR named four families of remote fridge controllers once the French wave spread beyond one vendor, and said putting a management interface on the internet is contrary to good practice. Its advice splits in two. If the box is not yet taken, pull every public IP, check the insurance contract before you cut the data feed back to the cooling contractor, review defrost ranges, and restore access only through a VPN or a protected network. If it is taken, do the same pull-off, then restart or factory-reset a Danfoss unit and rebuild it on the protected path.
THE FOUR FAMILIES IN THE FRENCH ALERT
- Danfoss AK-SM: Shop-level system managers, including current 800A units and older 800 boxes that stopped getting security fixes in May 2021.
- Danfoss AK-SC: Older controllers, including the AK-SC 355 line discontinued in 2016, with no patch stream left.
- Copeland xweb: Added to the alert on October 13 after the first Danfoss-only notice.
- Dixell xweb: Added the same day; CERT-FR pointed operators at Dixell’s own hardening note for those supervisors.
A factory reset, the alert says, is not enough on end-of-life gear. Persistence from a past break-in may go, but the box stays weak and will almost certainly be taken again if it goes back online. For live Danfoss kit the hardening list is dull on purpose: new firmware, Strict security mode, and no default passwords. Copeland had already issued firmware 1.13 for XWEB Pro after a separate set of bugs. The November victims look like the shops that skipped that homework, plus the ones whose hardware can no longer receive it.
The Rest of the Cold Chain Uses the Same Kit
Richard Horne, head of the UK’s National Cyber Security Centre, said British retailers should update software on fridge temperature controls, and that his team had seen a couple of UK cases where vulnerable technology had been exploited. He also said the country is likely to face an AI-powered attack on critical national infrastructure within two years, a separate warning from the grocery wave. On the food side his point was wider than the high street.
It’s not just supermarkets, it’s through the whole food supply chain, and we’ve been working through the night alerting organisations where we can see they’ve got exposed technology that’s vulnerable in this way.
Richard Horne, head of the National Cyber Security Centre, on BBC Radio 4’s Today programme
The same class of controller sits in warehouses, processing rooms and contractor yards, which is why a scan of StoreView pages is a food-system problem and not only a retail IT problem. Claroty built the AK-SM 800A research around that fact: one management page coordinates many field devices, so a session on the web interface is a session on the cold rooms behind it. Censys still counted just over 1,000 StoreView panels on the public internet in its November pass. CERT-FR has already said that putting an unpatched, end-of-life controller back online after a factory reset leaves it open to being taken again. Belgian prosecutors and national cyber teams are still trying to name who turned the dials on November 2.

Ken Urker’s Accidental Overdose Leaves His Finders Waiting

A Third Carrier Arrives as Hormuz Tankers Keep Burning

Shoe Prices Hit a Record as Flagship Pairs Stay Put

Nvidia’s First Call Without Huang Tests the Money Machine

Blake Griffin Says Oklahoma City Taxpayers Bought a Thunder Arena

Warsh Rejects Rate Guidance and Still Moves Markets

Davina McCall Reveals Cardiovascular Disease After Cholesterol Warnings

Dana-Farber Exits an MGB Medicare Advantage Network Early

NASA Launches the Roman Space Telescope’s Cosmic Bet

OpenAI’s Cyber Letter Puts the Defense Bill on Governments
-
 BUSINESS3 months ago
Warsh Rejects Rate Guidance and Still Moves Markets
-
 ENTERTAINMENT4 weeks ago
Davina McCall Reveals Cardiovascular Disease After Cholesterol Warnings
-
 BUSINESS2 months ago
Dana-Farber Exits an MGB Medicare Advantage Network Early
-
 NEWS3 months ago
NASA Launches the Roman Space Telescope’s Cosmic Bet
-
 NEWS3 months ago
OpenAI’s Cyber Letter Puts the Defense Bill on Governments
-
 NEWS3 months ago
Russia Recycles Its Old Warning Over Storm Shadow Plants
-
 ENTERTAINMENT2 months ago
Primetime’s $2.7 Million Preview Tops Pitt’s Costlier Film
-
 BUSINESS3 months ago
Jet Drones Lock Down Kyiv and Strip Kherson of Heat